Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required
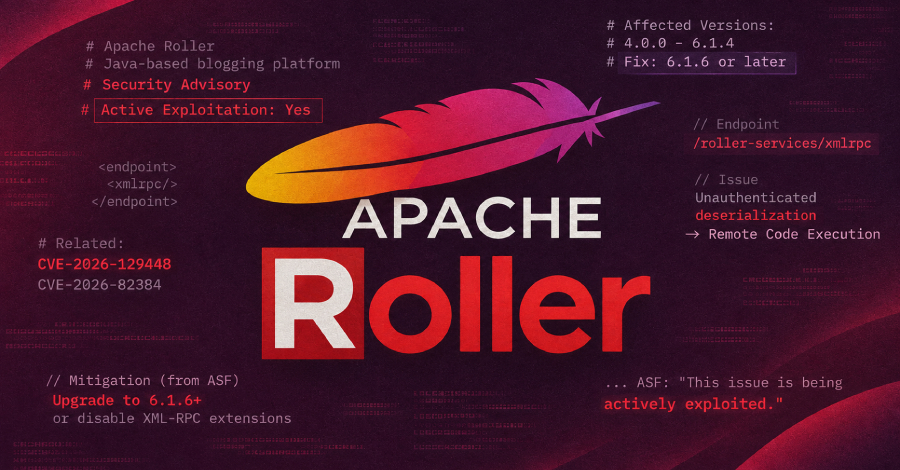
A critical security flaw in Apache Roller, an open-source, Java-based blogging platform, has come under active exploitation in the wild, according to the Apache Software Foundation (ASF)
The vulnerability, tracked as CVE-2026-129448 (CVSS score: 9.8), is a case of unauthenticated deserialization in the XML-RPC endpoint that could lead to remote code execution.
“Deserialization of Untrusted
The post “Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)