ClickFix Attackers Exploit Siemens Software Center Flaw to Deploy Remote Access Trojan
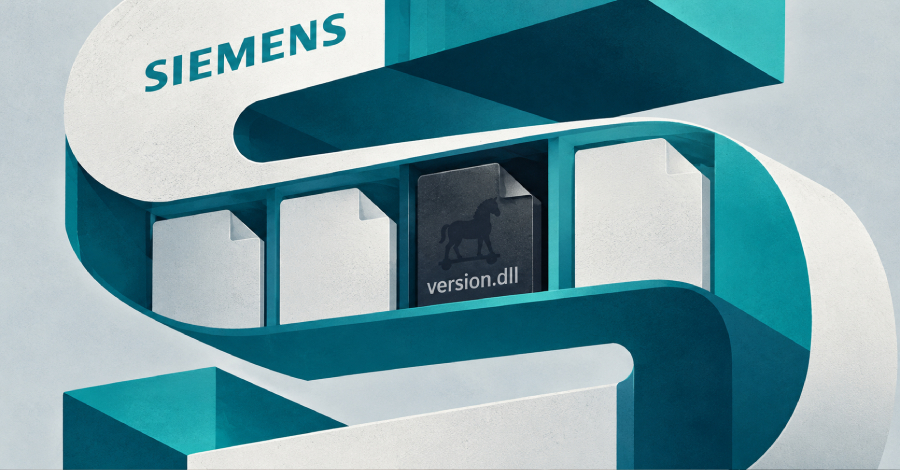
Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks.
The high-severity vulnerability, tracked as CVE-2026-110936 (CVSS v4 score: 8.4), could allow an attacker to place a specially-crafted DLL in a directory the application searches, resulting in execution of malicious code with the same privileges as the
The post “ClickFix Attackers Exploit Siemens Software Center Flaw to Deploy Remote Access Trojan” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)