Bitter Hackers Deploy New PapRAT Backdoor in Cyberespionage Campaign Targeting South Asia
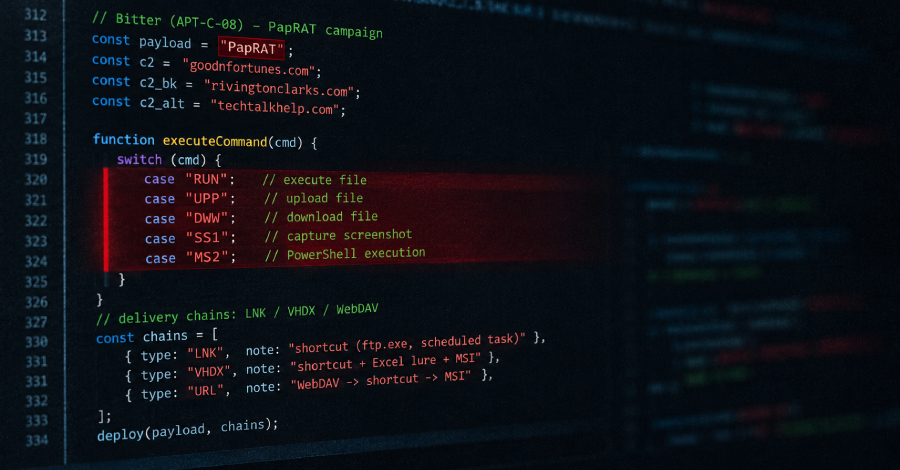
The South Asian cyber espionage group known as Bitter (aka APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397) has been observed targeting South Asian organizations with a previously unreported remote access trojan called PapRAT.
“PapRAT has both C++ and Rust implementations,” Fortinet FortiGuard Labs researcher Cara Lin said. “Its capabilities include command execution, file
The post “Bitter Hackers Deploy New PapRAT Backdoor in Cyberespionage Campaign Targeting South Asia” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)