Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
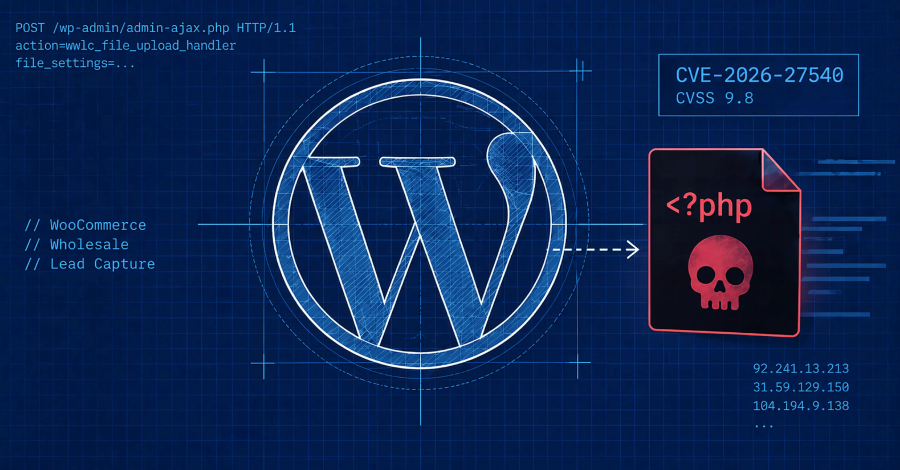
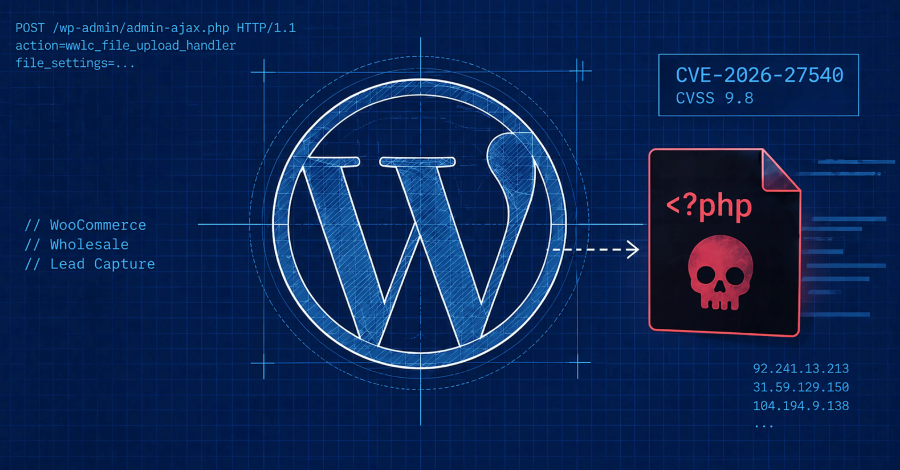
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs.
“This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execution,” Wordfence said.
The WordPress security company said it has blocked over 100,000 exploit attempts targeting the vulnerability since June 2026, with 99 of those attack attempts recorded over the past 24 hours. The vulnerability is tracked as CVE-2026-27540 (CVSS score: 9.8).
The issue is a case of arbitrary file uploads due to missing file type validation in an AJAX action named “wwlc_file_upload_handler” that impacts all versions of the plugin up to, and including, 2.0.3.1. This opens the door for an unauthenticated attacker to upload arbitrary files on the affected site’s server, paving the way for remote code execution.
In the attack observed by Wordfence, threat actors have been observed submitting crafted requests to the “wwlc_file_upload_handler” AJAX action with a forged file_settings parameter and a malicious PHP file (“shell.php”).
The uploaded PHP file is a web shell that reports host details and offers a browser-based upload form for writing additional malicious files to the compromised WordPress site. Attack attempts have originated from the following IP addresses –
- 92.241.13.213
- 31.59.129.150
- 2a0f:85c1:840:5389::1
- 92.241.13.140
- 23.137.105.214
- 23.180.120.140
- 104.194.9.138
- 187.75.114.36
- 114.10.43.203
- 37.114.144.209
Because a successful attack permits an attacker to upload arbitrary PHP files, WordPress site owners are advised to check for unexpected or recently created .php files, mainly in the uploads directory, and review for suspicious requests to “/wp-admin/admin-ajax.php” with the action parameter set to “wwlc_file_upload_handler” from the above IP addresses.
Critical Flaw in The Events Calendar
The development comes as Wordfence detailed two critical flaws impacting The Events Calendar, a WordPress plugin installed on over 600,000 websites. Successful exploitation requires the target event page to have comments enabled and the plugin’s “Show comments on event pages” option to be active. A brief description of the vulnerabilities is below –
- CVE-2026-78159 (CVSS score: 9.8) – A vulnerability arising from insufficient validation of the widget ‘classes’ map in the “parse_array” function that could be exploited to achieve unauthenticated remote code execution (Affects versions <= 6.17.3)
- CVE-2026-78006 (CVSS score: 9.8) – A vulnerability arising from insufficient protection in the “is_safe_widget_instance” function that could be exploited to achieve unauthenticated remote code execution (Affects versions <= 6.17.4)
“Both chains begin in the plugin’s widget-rendering pipeline and can ultimately lead to remote code execution without authentication through two separate methods,” Wordfence said.
“The first chain uses PHP Object Injection to execute arbitrary operating system commands on the underlying server. The second chain bypasses the object-injection guard and abuses an arbitrary-callable primitive to reset an administrator’s password, after which an attacker can upload a malicious plugin and take complete control of the site.”
Wordfence has warned that both chains can be triggered through WordPress’s pending-comment preview without moderator approval, and that the flaw could lead to complete site takeover, sensitive data theft, and malware deployment. StellarWP, which develops the plugin, has addressed the flaws in version 6.17.3.1 and 6.17.4.1, respectively.
The post “Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)