Hackers Exploit Critical Xen Orchestra Auth Bypass Flaw to Gain Admin Access
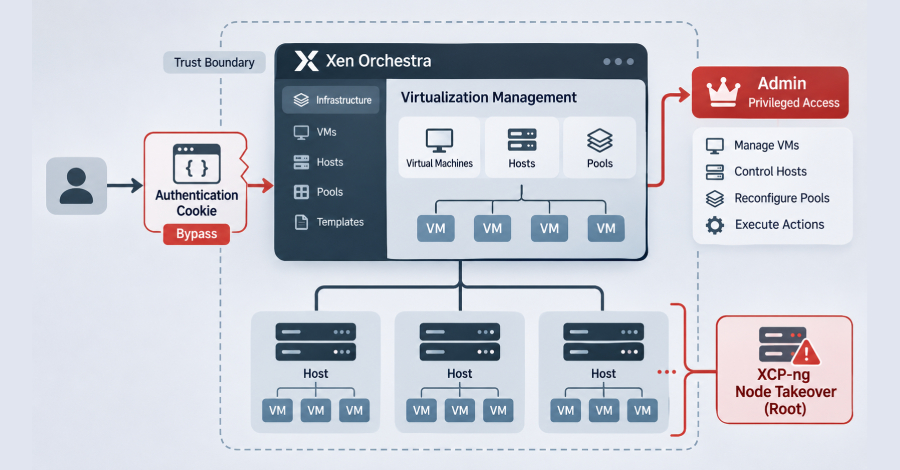
French software company Vates VMS has warned of a critical security vulnerability in Xen Orchestra that it said is being actively exploited in the wild.
The authentication bypass flaw, which does not yet have a CVE identifier, is tracked as VSA-2026-062.
“REST cookie parsing turns authenticationToken=j:%7B%7D into {},” Vates VMS said in an alert. “REST authentication passes that object to the
The post “Hackers Exploit Critical Xen Orchestra Auth Bypass Flaw to Gain Admin Access” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)