CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades
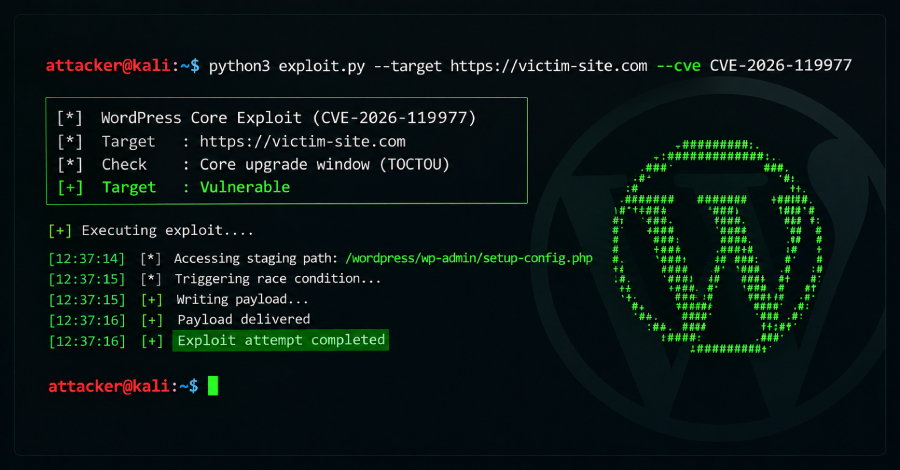
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation.
The high-severity vulnerability, tracked as CVE-2026-119977 (CVSS score: 8.1), is a case of Time-of-check Time-of-use (TOCTOU) race condition that could be exploited to achieve arbitrary code
The post “CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)