Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts
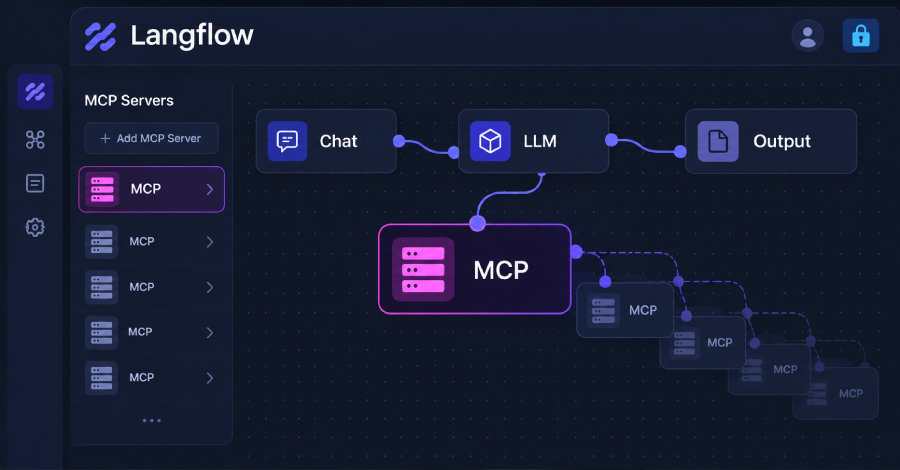
Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian.
Langflow is an open-source platform that allows developers to build artificial intelligence (AI) applications and agentic workflows. In February 2025, DataStax, the parent company of Langflow, was acquired by IBM.
The vulnerability in question is CVE-2026-105740 (CVSS score: 9.9), a case of
The post “Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)