Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave
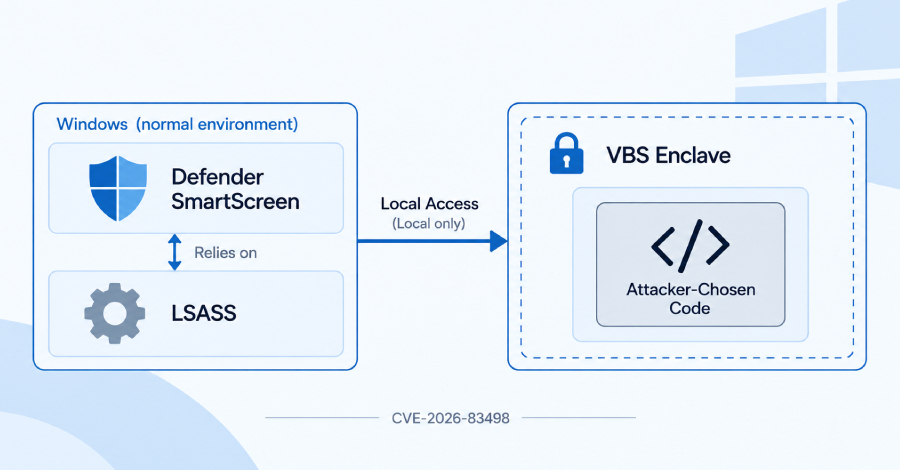
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over.
The protected area is a VBS enclave, an isolated slice of memory the operating system uses to guard secrets, and the one they broke into handles passwords for a Windows anti-phishing feature.
The work was done in a lab as a proof of
The post “Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave” appeared first on The Hacker News
Source:The Hacker News – [email protected] (The Hacker News)